Showing posts with label windows. Show all posts

Friday, 19 November 2010

Automatic logon in Windows systems

For process automation it can be handy to have scripts running to restart machines after installing update packs, or just for regular maintenance. One trick that I have found really handy when I restart a server, is to have it log on automatically. But this is only one application for automatic logon. Shared workstations, terminals, remote machines are all areas where it is potentially useful.

In this post, I'll outline a few way to manage your accounts to allow automatic login either locally or remotely.

First of all, if you have administrative rights, you can use User Account Control to remove the need for users to log in using a password.
  • To do this, go to Start -> Run -> enter "control userpasswords2"
  • In the User Accounts window, un-check "Users must enter a user name and password to use this computer"
  • That's it.

On a related note: If you manage several computers, you may wish to save passwords for all of them locally, so that you can easily administer them from your computer, without leaving them unsecure by removing the password on each machine:
  • Open the User Accounts window as step 1 shows.
  • Under the Advanced tab, click Manage Passwords.

  • You can use the Stored User Names and Passwords windows to store credentials for servers, websites and programs:
  •  It goes without saying, make sure your PC has a strong password if you are going to use it to store credentials for several websites and servers.

Lastly, for those who prefer to do things themselves, you can edit the registry to allow windows to automatically log in. The registry keys you need to edit are in the folder HKEY_LOCAL_MACHINE -> SOFTWARE -> Microsoft -> Windows NT -> Current Version -> Winlogon.

You need to add the following keys - DefaultUserName, DefaultPassword, AutoAdminLogon. The first 2 of these string registry keys should beset to the username and password of the administrator account. AutoAdminLogon should be set to "1". 

This last method is best used either if you are the only person with access to the machine, or if security is not an issue with this machine - e.g.: with a shared workstation - because the password is shown to anyone who knows where to look in registry. You wouldn't want to do this with your personal laptop where you store private information.

Hope this helps ;)

Tuesday, 25 May 2010

Disable the Welcome screen in Windows

The welcome screen is something I find annoying - I don't really like the look of it. A good enough reason to disable it then! To turn it off, so that you can log on and log off using the classic login prompt:

  1. Open the Registry editor (Start->Run->Regedit) and go to HKEY_LOCAL_MACHINE\Software\Microsoft\Windows NT\Current Version\WinLogon 
  2. Change the value for LogonType, from a "1" to a "0". you can guess that 0 gives Classic Mode and a 1 shows the Welcome Screen.  If there is no LogonType key, add it manually as a String-type key.
  3. Exit the registry editor when you are finished.
  4. Restart and you should be done.
Note that you must be an administrator on the computer / domain to make these registry changes.

Friday, 12 March 2010

Granting permissions to another computer in Windows

Hello there!

Do you ever get confused about which user to grant permission to on a specific folder?

What if you want to simply want to grant any access requests from another computer? (perhaps the other computer is a front end server - in web hosting, it's common practice to store your static files on another server).

One other reason to do this is so that you don't have to set up asp.net impersonation to give your asp.net website access to a network resource (the most common way of doing asp.net impersonation is storing cleartext passwords in web.config, which is kinda frowned upon).

Well, all you need to do to work around all the above issues is give the other computer itself permissions, then any user on the other computer will inherit the permissions (like the network service/aspnet user, for example):

  1. Open up the permissions/properties dialog for the folder (XP/2003 dialog shown below - in Vista/2008 you would right click and go to Sharing/Permissions).
  2. Click Add.
  3. By Default, the only "objects" you can share with are Users, Groups and Security Principals.
  4. Click on the "Object Types" button and check "Computers".
  5. Under "Enter the object names to select", type the other computer's name followed by a dollar ($) sign. For example "WEB$".
  6. Click "Check Names".
  7. Once the name is verified, click OK. You will now see something like this:


Now just set up your permission - this depends on what you want the other computer's users to be able to do (in my case any user on the WEB server). At the most, you should only need to give read and write access. Higher permissions like List Folder Contents, Modify and Full Control should only be granted to the Administrators group.

By the way, if you're running IIS7 remember to set the Application Pool to use the NETWORK SERVICE user, not the default IUSR, or this won't work. I'll detail how and why in a future post.

Monday, 24 November 2008

Installing an SSL certificate on IIS

An SSL certificate is used when a website wants to encrypt information between itelf and the end user. Whenever you see "https" at the start of a page's address, this means the site is using SSL. If you administer the server and want to use SSL to encrypt part, or all of your site, here is what to do:

First, you need to decide whether you want a self-signed or trusted certificate. A self-signed certificate is one that you create yourself within IIS. With a self-signed certificate, you are effectively saying "You can trust me". However, you can't be trusted.

It's nothing personal, it's just that browsers won't trust that you (your server) are who you say you are, for security purposes, unless you use a Trusted certificate. This is for the benefit of everyone on the web. All this means that if you have a public-facing website with a self-signed certificate installed, visitors to your website will see this message:


Not good. For anything other than testing/debugging, you will need a Trusted certificate. Where does one obtain such a thing? Why, from a Trusted Authority of course. Such as:
Before you buy a certificate, you'll need to create a Certificate Signing Request (CSR) in IIS. Microsoft has a simple guide to creating a certificate request. Once you have generated the CSR file, back it up mmediately. You'll find out why later. If you already have a self-signed certificate installed and want to replace in with a Trusted one, click here.

Now go ahead and buy the certificate you need. The trusted authority will need to be sent the text file that you generated during the certificate request. I'll leave that up to you. By the way, there's the obvious question that you may be asking - "Can I trust the trusted authority?". The trusted authority does some checks to ascertain that you are legitimate, or your business is legitimate. Can they be trusted to do this. In short, yes. They are vetted by internet authorities - becoming a trusted authority is not easy, and their business is built on their reputation, so it is in their interest to do their job as they should.

Anyway, I digress. At this point, assuming you aren't selling arms to rogue states, you will have passed the checks and the trusted authority will have sent you your certificate details. This email will include a long string of text called the "Certificate Signature" or "Global Server ID". This, effectively, IS the certificate. Here's what you need to do to use it (to replace an existing self signed certificate, see the next section...):
  1. Copy the certificate signature into a new text file in notepad; save as a .txt file.
  2. Rename the .txt file - change the extension to .p7b.
  3. Move this file to your server, and process the pending request through IIS:
  4. Open Internet Information Services Manager.
  5. Browse to the website or Virtual Directory that you plan to secure.
  6. Right-click on the site/directory, then click properties.
  7. Click the Directory Security tab.
  8. Under Secure Communication click Server Certificate.
  9. In the Website Certificate Wizard, click Next.
  10. Choose to Process The Pending Request and Install The Certicicate, then click Next. The pending request must match the response file. If you deleted the Pending Request in error, you will have to generate a new CSR and replace the certificate. Not good if you've just spend a couple o' hundred big ones.
  11. Select the location of the certificate response file (p7b file) then click Next.
  12. Enter your SSL port (normally 443).
  13. REad the summary screen to be sure you are proccessing the correct certificate, then click Next.
  14. You will now see a confirmation screen. When you have read it, click Nex.
  15. You're done!
If you are all done, then well done! Digg this post if this post helped you. Now, at this point some of you may be thinking: "Wait! I was developing my site, so I already have a self-signed certificate installed. How do I REPLACE it with a trusted certificate?".

Here's how:
  1. Leave the site with the installed certificate alone.
  2. Create another virtual site with in IIS (does not have to be a functional site)
  3. Enter properties for the newly-created virtual site, then go to the certificate wizard to create a new certificate request. If you are renewing a trusted certificate, the information you enter on this CSR must exactly match the information on your production certificate, since the new CSR will be replacing it.
  4. When you receive your new certificate, install this certificate into the new virtual site that you created (follow the process above).
  5. Now delete the new virtual site.
  6. Go to your target web site. Use the certificate wizard - select Replace the Current Certificate. Choose the new certificate from the list.
  7. (Optional) When convenient, delete the old certificate using Microsoft Management Console (mmc). Add the Certificate Snap-In and delete the old SSL certificate.
  8. You're done!
I have tried to explain everything fully, since it is quite a complicated process. Please comment if you need any clarifications or any other help. If you found this post useful, Digg it using the link at the top, or subscribe to the feed.

Cheers!

Sunday, 26 October 2008

Automating tasks in Windows

If you find yourself endlessly performing monotonous tasks as part of your admin work, you may be able to leverage your operating system's built-in automation mechanism. Tasks ideal for this include backup, tidying up filesystems and automated messaging. (Windows also includes a standalone backup program, which I will cover in another post.)

In Windows and Linux, the mechanisms for automating tasks are quite different, so in will cover Linux in a future post. In windows, you typically write an application/script, then run it as a Scheduled Task. If you need to run a task when the computer starts, or before you login, or even automatically login, or run it continuously in the background, there are other options, which I will cover in another post.

Windows Scheduled Tasks

Once you have a program or script that you want to automate, go to Programs -> Accessories -> System Tools -> Scheduled Tasks. In the window, double-click Add Scheduled Task. Click next, then click Browse to choose your program (sorry about the blue lines):

Once you have chosen the task, click Next. Next, select the scheduling of your task - Daily, Weekly, etc. Don't worry about choosing the wrong option here, as we can configure the scheduling in the Advanced Options.

You will also be prompted for your username and password. Enter your username in the format Computer Name/Username. You can find your computer name by right-clicking My Computer and selecting the "Computer Name" tab. It is next to "Full Computer Name".

Click next, and you should see the following screen:

If you are happy with the simple scheduling options you have just chosen, go ahead and click Finish. If you want to tweak the schedule, check "Open advanced properties..." then click Finish.

Let's take a look at the options available in the advanced properties.
First the Task tab:
Run: Here you specify the executable or script to run at the scheduled times (I have used Character Map as an example). You probably won't need to change this unless you have made a mistake in one of the previous steps. If you need to add arguments to your program, add them here (eg: ...\myprog.exe -verbose -init). Remember, however, that if the path to your program contains spaces, this cause problems (e.g.: you may have your program under "Documents and Settings\...". Windows assumes that spaces are separators, and will therefore complain that "Documents is not a program... etc". To get around this, just enclose your path in quotes. For example:
"C:\Documents and Settings\Username\Adminprogs\cleanup.exe" -auto -init. Note that the arguments are outside the quotes.

Start in: Normally, the path to the folder containing your program/script. If you program uses other files, you can add the paths to these here - separate paths with commas.

Comments: You can add information in here for other system administrators to read.

Run As: This is the Computer/Username combo again. You can usually just run this as yourself - you may wish to create a new non-admin user just to run tasks like this. Note that if the password is changed for this user account, the scheduled task will stop working. You can use the "Set Password" button if this happens.

Run only is logged on: Self-explanatory.

Enabled: Self-explanatory. You can uncheck this box to temporariliy disable the task.

Now, the Schedule tab:
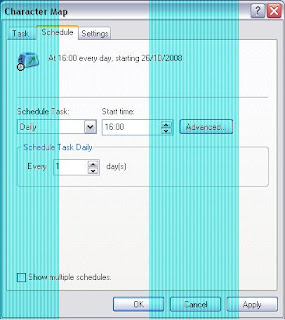
Most of this tab is self-explanatory, but there are a lot of possibilities here, so I will work through an example using a typical schedule. I will configure the task to run at 1am and 1pm on weekdays.

There are 2 ways to do this.
  1. Schedule the task "Weekly", choose Mon-Fri from the options, and from the Advanced schedule options choose to repeat the task every 12 hours until 13:01. The reason we choose 13:01, not 13:00 is because we want to make sure the task runs at 13:00, then we can stop repeating it. You should end up like this:
  2. Now the alternative. Again, schedule the task weekly and select Mon-Fri. However, instead of repeating the task, add a 2nd schedule - every week day at 13:00. So now your task has 2 schedules - every weekday at 01:00 and every weekday at 13:00. To do this, check "Show Multiple Schedules" and click "New..." at the top. Set the Start Time of this sub-task to 13:00:
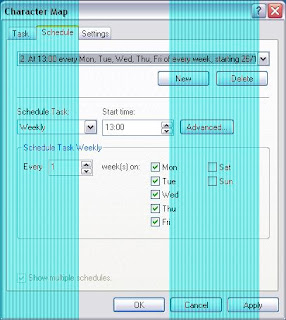
Now, the Settings tab:

The options hereare mostly self-explanatory. Choose whatever suits you. One that I will comment on is the "Stop the task if it runs for..." option. If your program/script has a tendency to hang, you may want to set this option to prevent it from using up system resources or crashing the computer.

Press OK. You may be prompted to enter your password. That's all!

Friday, 24 October 2008

Forcing restart in Windows and Linux

Sometimes it becomes necessary to restart a server or other remote system. Windows is especially problematic, as it will often wait on a hung application to end before shutting down.

Thankfully, there is a command to help, the "shutdown" command. If you are remotely logged in, simply open a command prompt (Start -> Run -> type "cmd" -> OK). In the command prompt, enter the following:

shutdown -t 0 -r -f

There are other options (to view them all, type "shutdown --help" into the command prompt); but I will summarise the ones above:
  • -t 0
    • This sets a timeout of zero seconds before shutting down
  • -r
    • This specifies a restart
  • -f
    • Forces all open programs to close immediately
In Linux, things are more immediate:

shutdown now -r

Enter the above command in a terminal window to force an immediate restart.